
• Home
  • About Us
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Terms & Conditions
Saturday, October 24, 2026
freevirtualsolutions.com
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management
No Result
View All Result
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management
No Result
View All Result
Free Virtual Solutions
No Result
View All Result
Home Enterprise Technology

AOMEI Supply Chain Attack Hijacked Update Servers

Ermias S. by Ermias S.
1 hour ago
in Enterprise Technology
0
399
SHARES
2.3k
VIEWS
Share on FacebookShare on Twitter


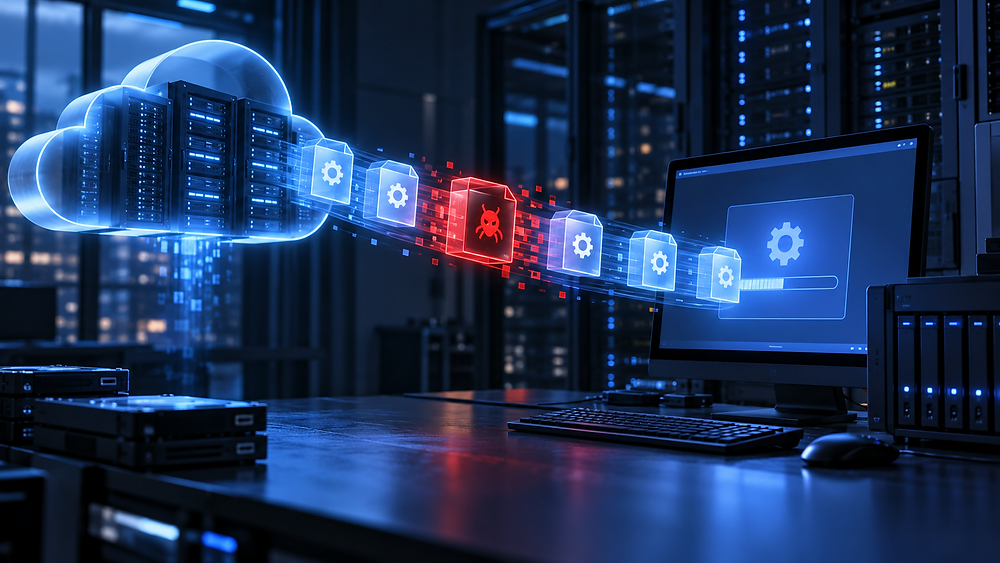
Attackers compromised AOMEI Technology’s software distribution infrastructure and used brief tampering windows to deliver malware through a trusted update mechanism, according to new research from Google and Mandiant.

Google Threat Intelligence Group and Mandiant tracked the activity as UNC7017. Researchers observed malicious changes lasting only five to ten minutes between April and July 2026. Systems checking for updates during those windows received attacker-controlled instructions, while later inspections saw legitimate files.

The campaign redirected AOMEI clients to a weaponized archive containing the CROSSROAD downloader. That component established persistence and deployed SHINYROAD, a modular backdoor. Researchers said the attackers also abused legitimate administration tools and changed infrastructure as the campaign evolved.

The short-lived modifications created a significant forensic challenge. A security team investigating after the event could visit the same update location and find only clean content, increasing the risk that an alert would be dismissed as a false positive.

AOMEI told the researchers it had taken corrective action to secure its distribution servers. That server-side response does not remove malware already installed on customer endpoints.

Organizations that ran AOMEI software during the April through July exposure period should conduct retrospective endpoint and network hunts using the published indicators. Defenders should focus on suspicious child processes from updater services, unexpected scheduled tasks and connections to infrastructure identified in the research.

The incident shows why signed software alone is insufficient when an update client accepts unsigned configuration changes or downloads content from destinations that are not tightly restricted.


Source_link

Tags: AOMEIattackchainhijackedServerssupplyUpdate
Previous Post

The Real Cost of One Bad Customer Conversation

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Categories

  • Customer Support (1,844)
  • Enterprise Technology (4,692)
  • Marketing Support (3,986)
  • Virtual Assistant (4,296)
  • Workforce Management (1,552)

Free Virtual Solutions

Welcome to freevirtualsolutionsThe goal of freevirtualsolutions is to give you the absolute best news sources for any topic! Our topics are carefully curated and constantly updated as we know the web moves fast so we try to as well.

Category

  • Customer Support
  • Enterprise Technology
  • Marketing Support
  • Virtual Assistant
  • Workforce Management

Recent Post

  • AOMEI Supply Chain Attack Hijacked Update Servers
  • The Real Cost of One Bad Customer Conversation
  • 3 Lessons From Building a Venture Fund That Can Help You Make Smarter Business Decisions.
  • Home
  • About Us
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Terms & Conditions

Copyright © 2023 Freevirtualsolutions.com | All Rights Reserved.

No Result
View All Result
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management

Copyright © 2023 Freevirtualsolutions.com | All Rights Reserved.

Chat with us

Hi there! How can I help you?