
• Home
  • About Us
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Terms & Conditions
Friday, November 13, 2026
freevirtualsolutions.com
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management
No Result
View All Result
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management
No Result
View All Result
Free Virtual Solutions
No Result
View All Result
Home Enterprise Technology

OpenSSH SSHole Authentication Bypass Exploited in Attacks

Ermias S. by Ermias S.
3 days ago
in Enterprise Technology
0
399
SHARES
2.3k
VIEWS
Share on FacebookShare on Twitter


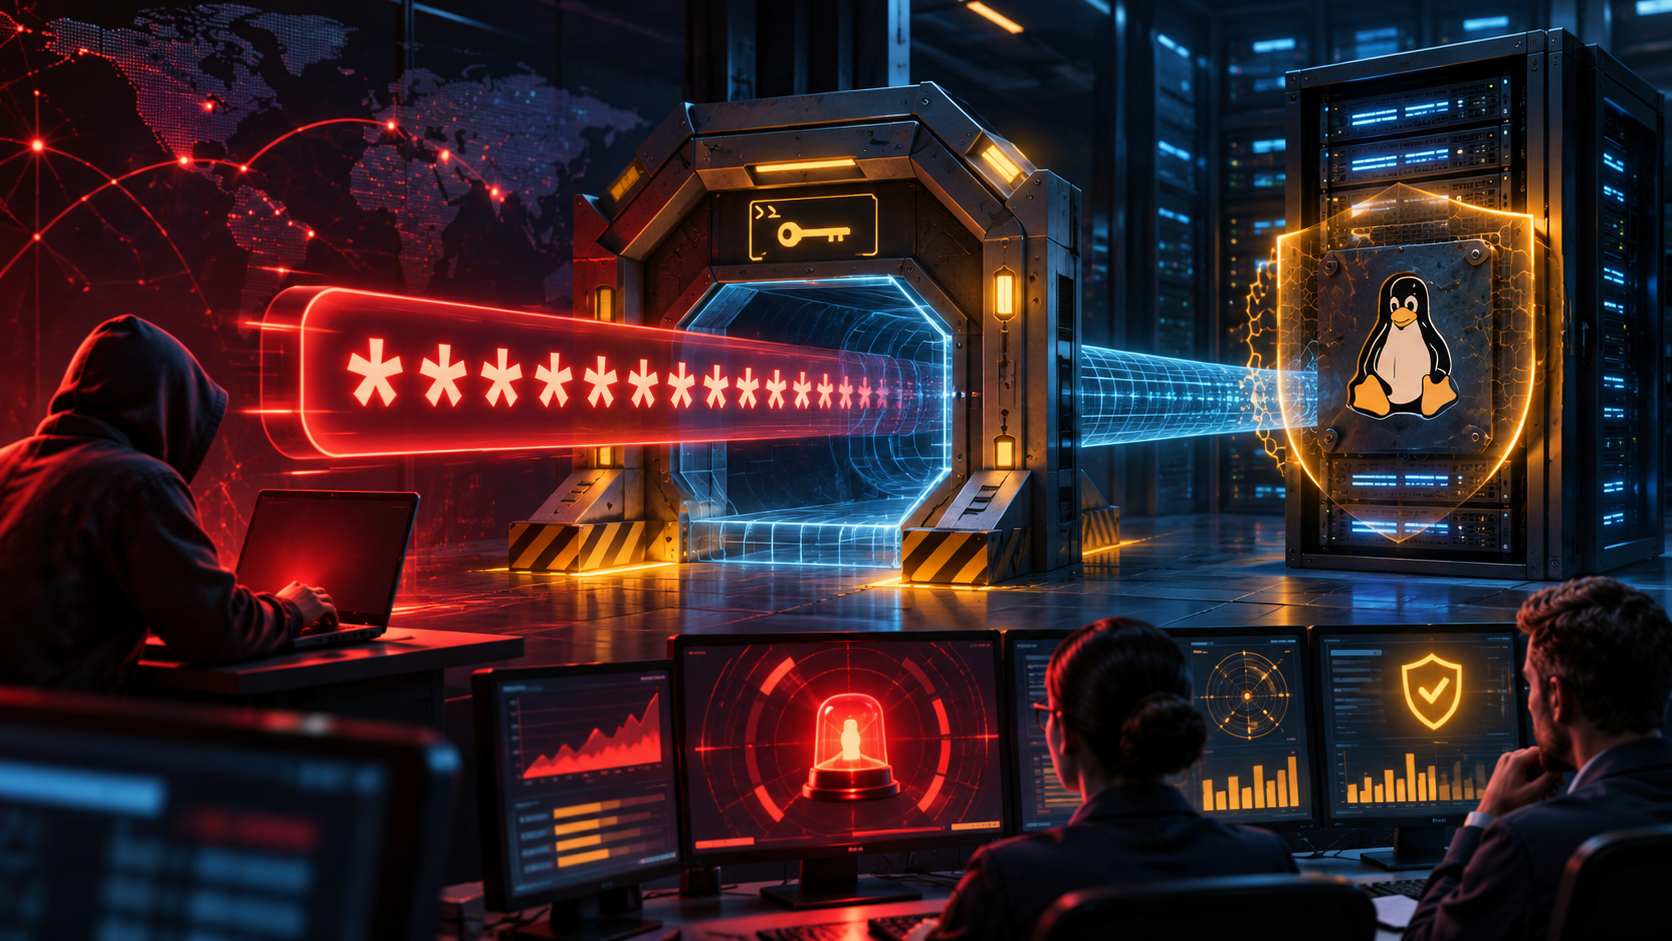
Attackers are exploiting a critical OpenSSH authentication bypass known as SSHole, targeting certain Linux systems built with musl libc and configured without Pluggable Authentication Modules. The flaw is tracked as CVE-2026-123158 and was fixed in OpenSSH 10.6p2.

The vulnerability can let an unauthenticated remote attacker bypass password authentication by submitting an overlong password. The affected configuration is common in lightweight distributions and embedded environments, including Alpine Linux, OpenWrt, Yocto and Buildroot. Red Hat said its products are not affected because they use glibc rather than musl.

SANS Internet Storm Center observed exploit attempts beginning November 5, while GreyNoise later reported successful chains that performed reconnaissance, queried cloud metadata, read sensitive files and added SSH keys. Early activity has included botnet and cryptocurrency-mining behavior.

The issue is especially dangerous because SSH is often exposed for routine administration and may sit on appliances that receive less attention than general-purpose servers.

Bri Frost, director of product management at Cloud Range, said: “SSH is a routine part of how organizations manage systems. That makes SSHole more than a patching task.” She added that teams should check for prior compromise and practice containment, not just install the fix.

Defenders should identify internet-facing SSH services, determine which use musl without PAM, upgrade to OpenSSH 10.6p2 or a vendor-fixed package, and review authorized_keys, authentication logs, new accounts and outbound connections.


Source_link

Tags: AttacksAuthenticationBypassexploitedOpenSSHSSHole
Previous Post

He’s Worth $10 Billion. Now He’s Betting on a New AI Startup.

Next Post

What market data reveals about AI search

Next Post
What market data reveals about AI search

What market data reveals about AI search

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Categories

  • Customer Support (1,900)
  • Enterprise Technology (4,770)
  • Marketing Support (4,053)
  • Virtual Assistant (4,383)
  • Workforce Management (1,559)

Free Virtual Solutions

Welcome to freevirtualsolutionsThe goal of freevirtualsolutions is to give you the absolute best news sources for any topic! Our topics are carefully curated and constantly updated as we know the web moves fast so we try to as well.

Category

  • Customer Support
  • Enterprise Technology
  • Marketing Support
  • Virtual Assistant
  • Workforce Management

Recent Post

  • EBONY CEO Eden Bridgeman Tackles What’s Next in Media
  • Learning from rejection | Seth’s Blog
  • iSolved HR Self-Service Made Easier with AI
  • Home
  • About Us
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Terms & Conditions

Copyright © 2023 Freevirtualsolutions.com | All Rights Reserved.

No Result
View All Result
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management

Copyright © 2023 Freevirtualsolutions.com | All Rights Reserved.

Chat with us

Hi there! How can I help you?