

In today’s rapidly evolving cyber threat landscape, attackers are using increasingly sophisticated tactics to bypass traditional email security tools. One of the most alarming trends is the rise of QR code phishing attacks, where malicious QR codes are embedded in email attachments—especially PDFs—to trick users into scanning them with mobile devices. These scams often lead to phishing sites, credential theft, and mobile device exploitation. In this blog, we’ll break down how QR code-based email scams work, why they’re so effective, and how organizations and individuals can protect themselves from this growing form of mobile-targeted cyberattack.
What Are QR Codes and Why Are They a Threat?
Quick Response (QR) codes are two-dimensional barcodes that, when scanned by a smartphone or tablet, direct users to various digital destinations such as websites, apps, contact information, and more. Their convenience and familiarity have led to widespread use in both personal and professional environments. Unfortunately, this same ease of use has also made QR codes an increasingly attractive tool for cybercriminals. Scanning a malicious QR code can direct users to phishing sites, fake login pages, or even trigger unwanted downloads that compromise devices and networks. The risk is increased because QR codes are inherently opaque: users cannot see or verify the link behind the code before scanning.
How Attackers Are Using PDFs with Customized QR Codes to Bypass Defenses
Traditionally, email security solutions rely on detecting harmful links, attachments, and malicious payloads within the email body. However, attackers have started bypassing these filters through a simple yet clever technique: embedding QR codes inside PDF attachments.
Here’s how it works:
Personalized Campaigns
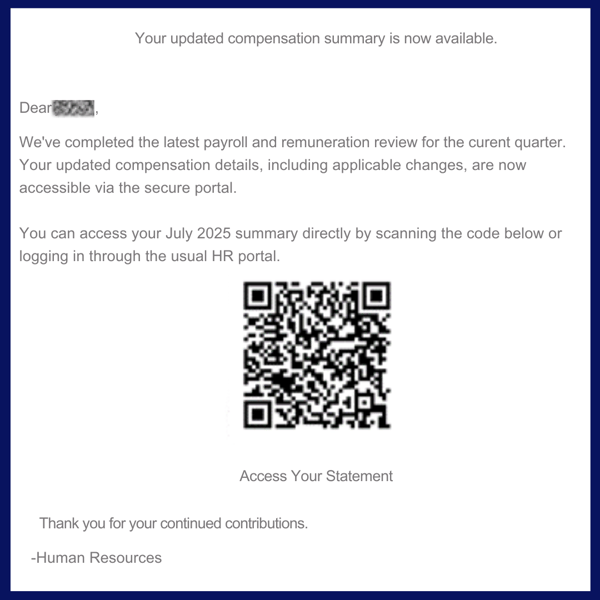
Attackers craft PDF files containing QR codes that are customized with the recipient’s company branding, name, or role. This increases user trust, making the PDF and its embedded QR code appear legitimate. Here is an example email that one of our iCorps employees received, and their username has been redacted for privacy:
Bypassing Filters
Most email security filters and sandboxing engines focus on detecting suspicious URLs or executables. QR codes, as images, often aren’t parsed or checked for harmful destinations—especially when embedded in PDFs.
Mobile Device Exploitation
As users often access emails on their phones, they may be more likely to scan a QR code with the same device, bypassing desktop protection layers.
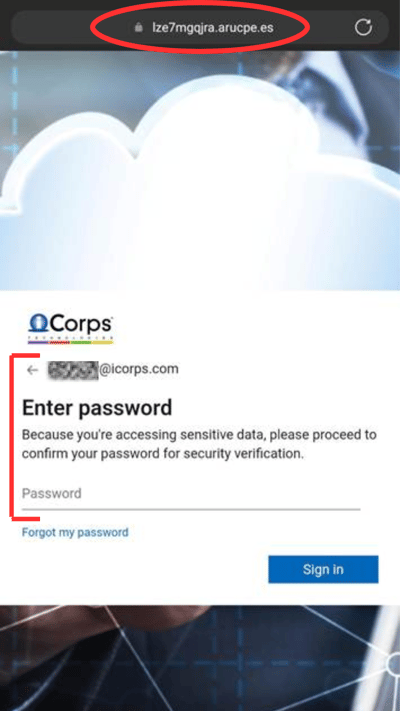
Credential Harvesting and Token Theft
Once scanned, users are directed to phishing sites mimicking familiar login portals. Victims might enter their credentials, giving attackers access to corporate accounts, or even approve OAuth token requests, enabling deep access without passwords.
The seamlessness, personalization, and psychological manipulation of these campaigns make them highly effective and dangerous.
The Double-Edged Sword of Mobile Convenience
Many organizations have strengthened desktop email security with solid solutions, but the increase in mobile device usage introduces new challenges. Employees, eager to fix issues or respond swiftly, often use their mobile camera to scan a QR code without hesitation. This switch from the relatively secure world of a desktop to the personal, less protected mobile environment gives attackers a significant advantage.
While security tools are evolving to identify suspicious QR codes and malicious PDFs, technological solutions will always be a step behind novel attack techniques. That’s why end-user education is critical:
As QR code-based attacks become more sophisticated and personalized, the responsibility to defend against them now rests on both users and organizations. A well-informed user is far less likely to become the next victim, which is why education remains the single most effective security control in this new era of digital threats.

