• Home
  • About Us
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Terms & Conditions
Monday, October 26, 2026
freevirtualsolutions.com
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management
No Result
View All Result
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management
No Result
View All Result
Free Virtual Solutions
No Result
View All Result
Home Enterprise Technology

StealC Returns as the Stadia Remote Access Trojan

Ermias S. by Ermias S.
6 hours ago
in Enterprise Technology
0
399
SHARES
2.3k
VIEWS
Share on FacebookShare on Twitter


The seller behind the StealC information stealer has returned with a modular remote access trojan months after international authorities disrupted the malware’s infrastructure.

Varonis Threat Labs identified the new malware as Stadia and said its code includes StealC components copied byte for byte. Researchers obtained the build shortly after it appeared for sale and tested its control panel against a laboratory system.

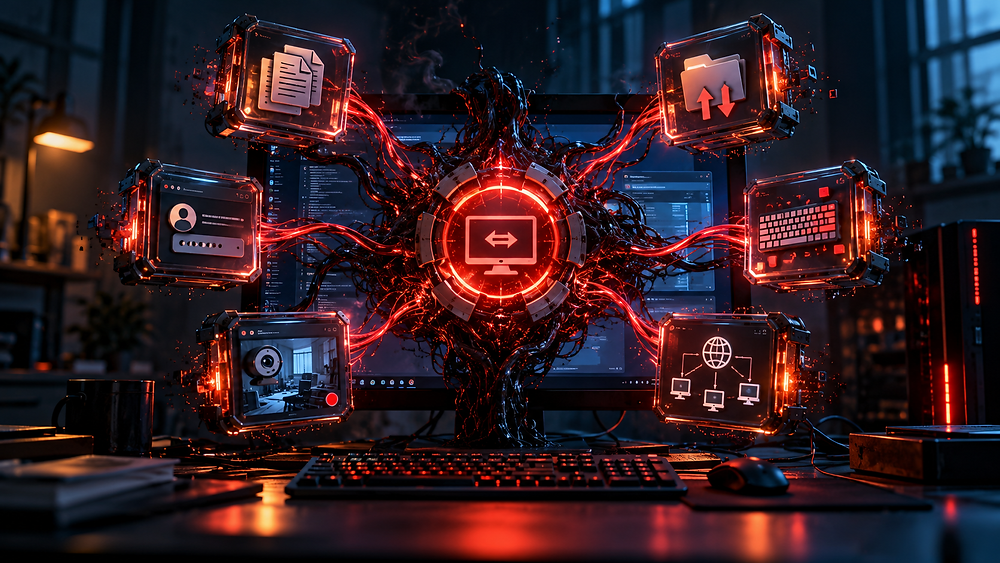
Stadia expands the operator’s capabilities beyond credential theft. Its six advertised modules include hidden desktop control, a remote command shell, file browsing, process management, an in-memory loader and the original StealC stealer. Hidden desktop functionality can allow an attacker to operate applications and authenticated sessions without displaying those actions to the victim.

The release follows the June 2026 phase of Operation Endgame, when Europol and its partners seized 326 servers and 142 domains associated with several malware families. Authorities said the StealC disruption involved credentials recovered from hundreds of thousands of infected systems.

Varonis found that the seller is attempting to rebuild its customer base by offering former StealC users one month of access to Stadia’s highest service tier. The move illustrates how malware operations can recover after infrastructure seizures when developers, customers and distribution channels remain available.

Defenders should monitor for unusual remote desktop behavior, unexpected command-shell activity, new scheduled persistence and credential access from user workstations. Organizations that previously encountered StealC should treat Stadia as a related threat rather than an entirely new malware family.


Source_link

Tags: AccessRemoteReturnsStadiaStealCTrojan
Previous Post

Beyond CSAT: What the Score Can and Cannot Measure

Next Post

How Much Does a Cold Calling Virtual Assistant Cost?

Next Post
How Much Does a Cold Calling Virtual Assistant Cost?

How Much Does a Cold Calling Virtual Assistant Cost?

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Categories

  • Customer Support (1,850)
  • Enterprise Technology (4,698)
  • Marketing Support (3,991)
  • Virtual Assistant (4,304)
  • Workforce Management (1,553)

Free Virtual Solutions

Welcome to freevirtualsolutionsThe goal of freevirtualsolutions is to give you the absolute best news sources for any topic! Our topics are carefully curated and constantly updated as we know the web moves fast so we try to as well.

Category

  • Customer Support
  • Enterprise Technology
  • Marketing Support
  • Virtual Assistant
  • Workforce Management

Recent Post

  • The Call Center QA Metrics That Actually Predict CSAT
  • Key Things That “Make or Break” a Resource Planning Team
  • How Much Does a Cold Calling Virtual Assistant Cost?
  • Home
  • About Us
  • Contact Us
  • Disclaimer
  • Privacy Policy
  • Terms & Conditions

Copyright © 2023 Freevirtualsolutions.com | All Rights Reserved.

No Result
View All Result
  • Home
  • Virtual Assistant
  • Enterprise Technology
  • Customer Support
  • Marketing Support
  • Workforce Management

Copyright © 2023 Freevirtualsolutions.com | All Rights Reserved.

Chat with us

Hi there! How can I help you?